Missing Authorization for Interactive Sessions
June 9, 2025

Products Impacted
This vulnerability is present in all versions of BackendAI. We tested on version 25.3.3 (commit f7f8fe33ea0230090f1d0e5a936ef8edd8cf9959).
CVSS Score: 8.1
CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H
CWE Categorization
CWE-862: Missing authorization
Details
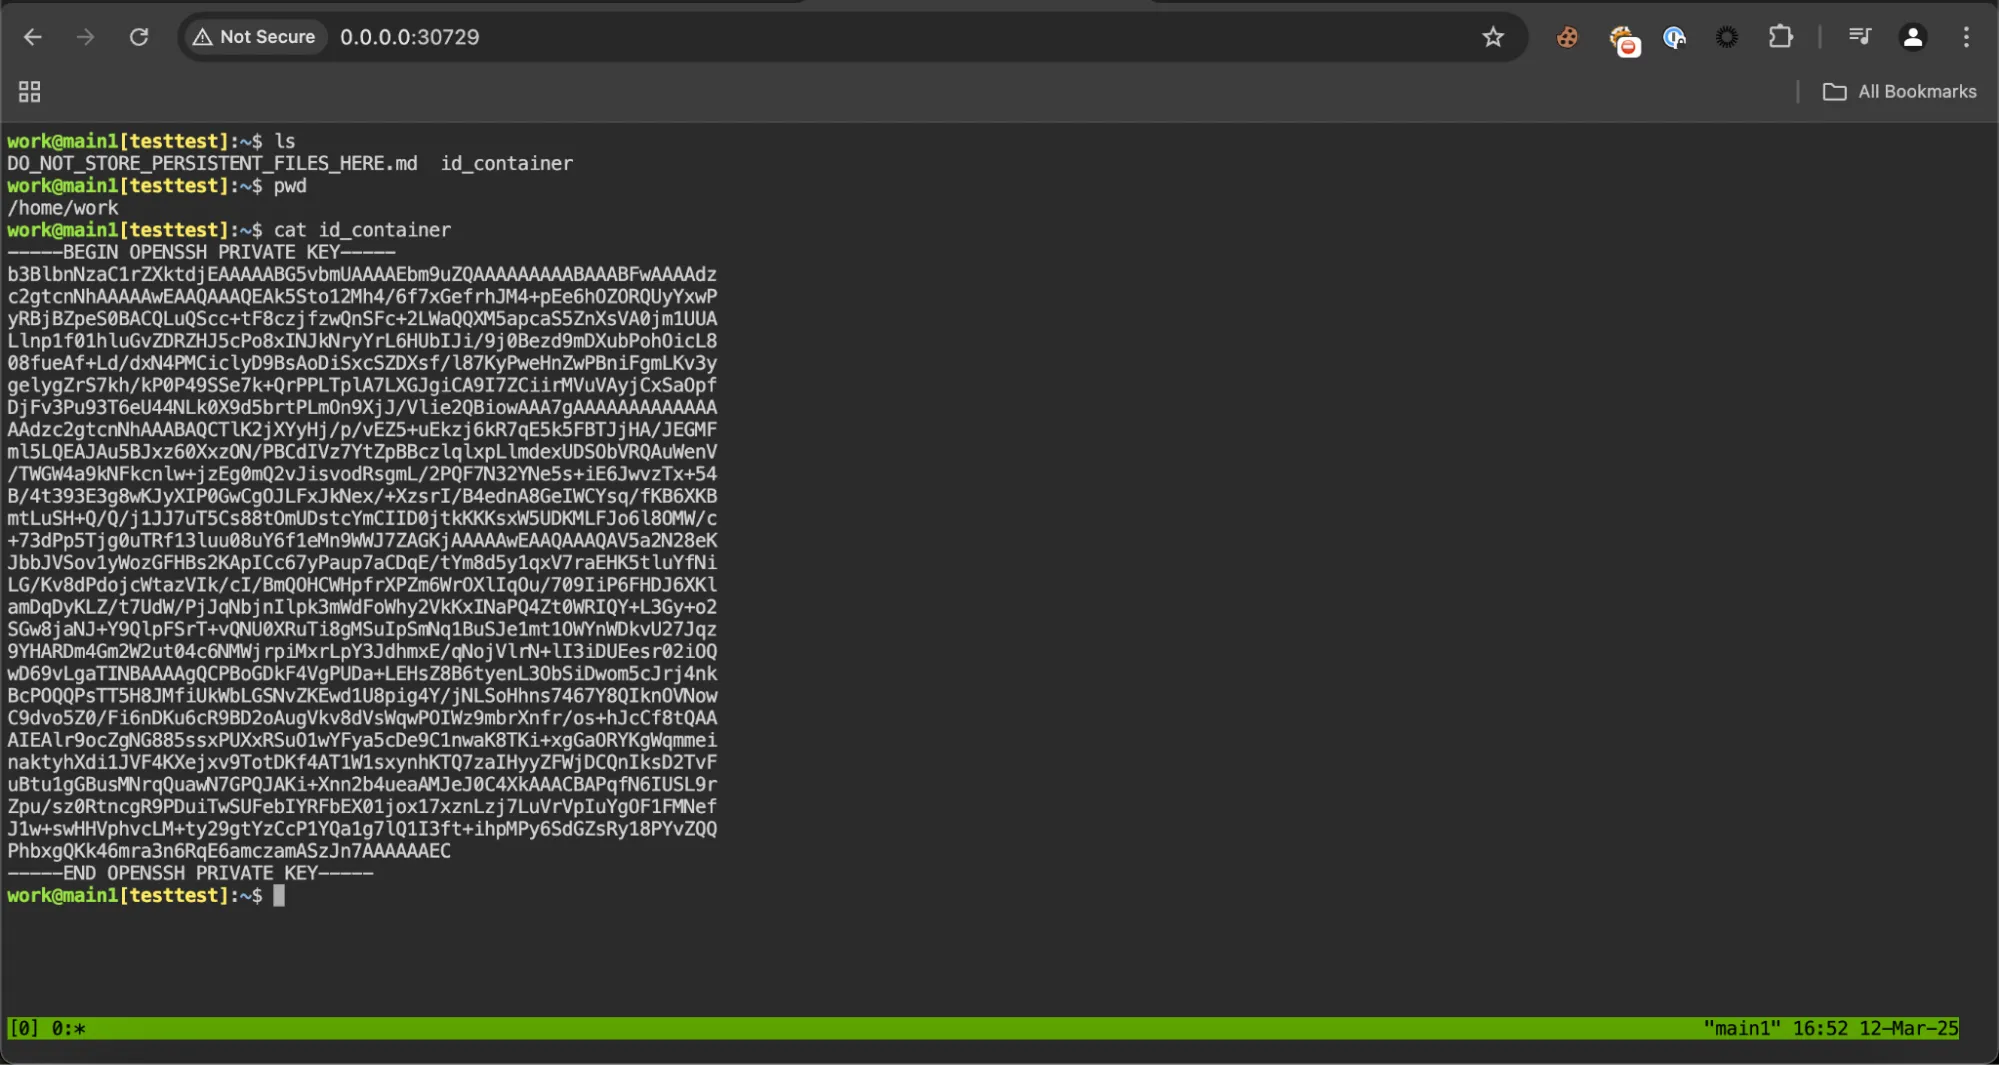
When a user starts an interactive session, a web terminal gets exposed to a random port. A threat actor can scan the ports until they find an open interactive session and access it without any authorization or prior authentication.
To reproduce this, we created a session with all settings set to default.
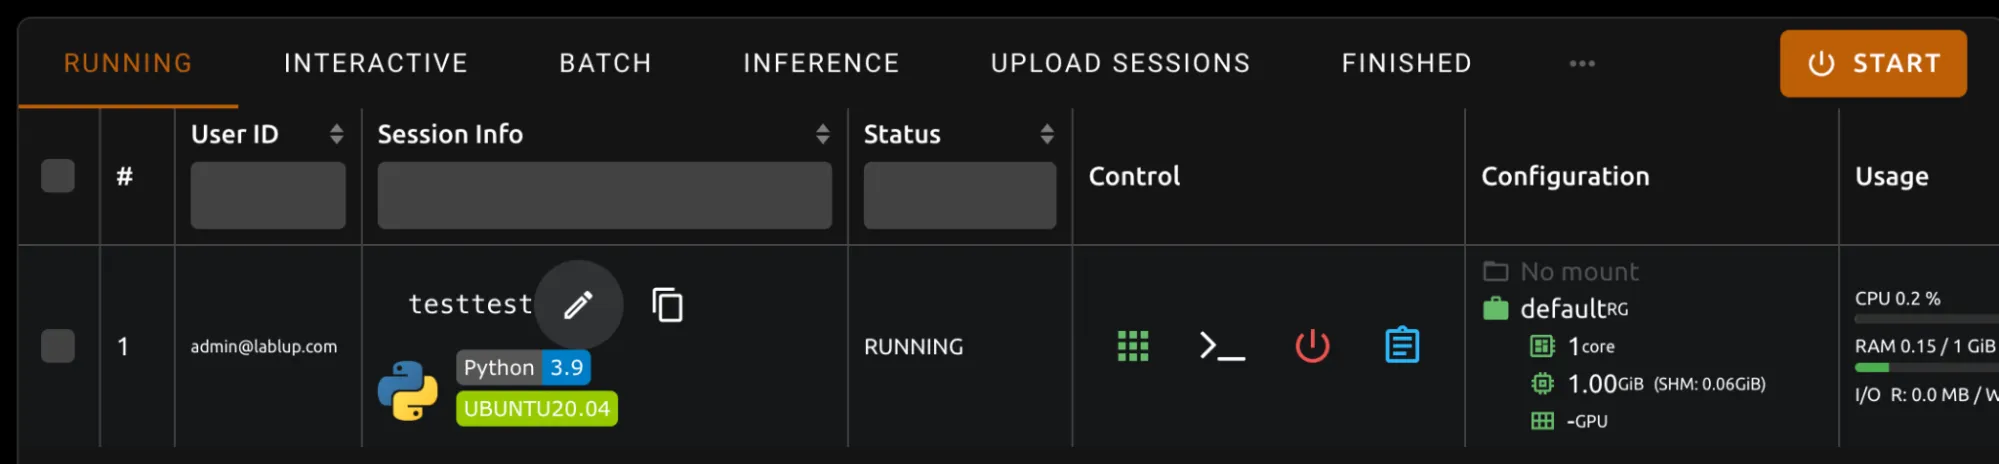
Then, we accessed the web terminal in a new tab
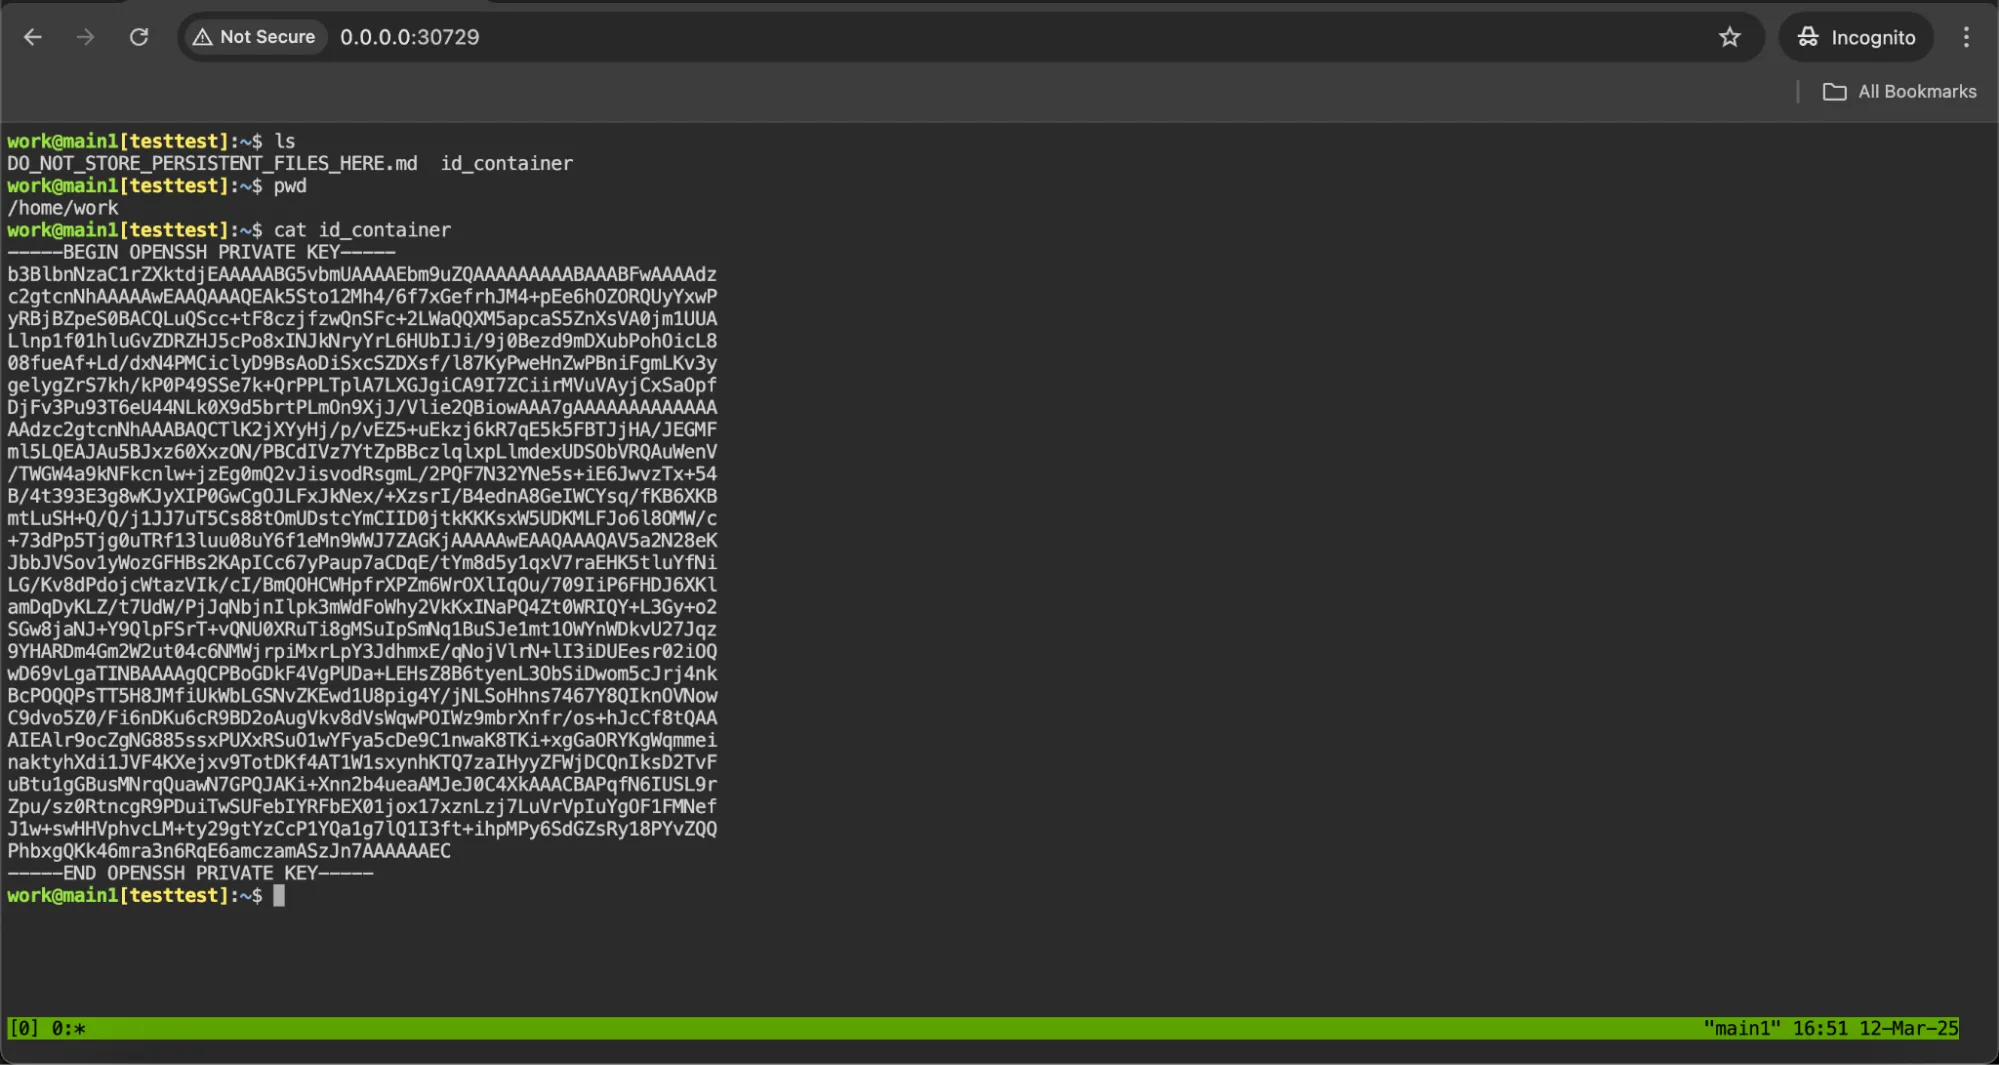
However, while simulating the threat actor, we access the same URL in an “incognito window” — eliminating any cache, cookies, or login credentials — we can still reach it, demonstrating the absence of proper authorization controls.
Related SAI Security Advisory
September 11, 2026
_READ_ONLY_COMMANDS_POSIX expansion adds 31 commands with no path checking, granting unconditional access to the full host filesystem
Mistral Vibe automatically approves a large set of commands that are not subject to the expected workspace path restrictions, allowing files anywhere on the host to be accessed without user approval.
September 11, 2026
Environment variable prefixes stripped from permission check enable RCE via env injection
Mistral Vibe does not consider environment variable assignments when checking whether a command can run without approval, allowing environment controlled behavior in allowlisted programs such as Git to be abused for arbitrary code execution.