Secure Agentic AI Systems
Gain visibility into agent behavior and capabilities, assess emerging risks, and enforce security controls across agentic AI workflows.
Trusted by Industry Leaders




Autonomous AI introduces real operational and security risks
Agentic AI systems plan tasks, execute actions, and use tools independently. This autonomy creates new attack surfaces and elevates the risk of prompt hijacking, unsafe execution, lateral movement between agents, and unauthorized access to high value systems. As agents gain access to additional skills and capabilities, security teams also need to know what those agents can do, which capabilities introduce risk, and which should be permitted.
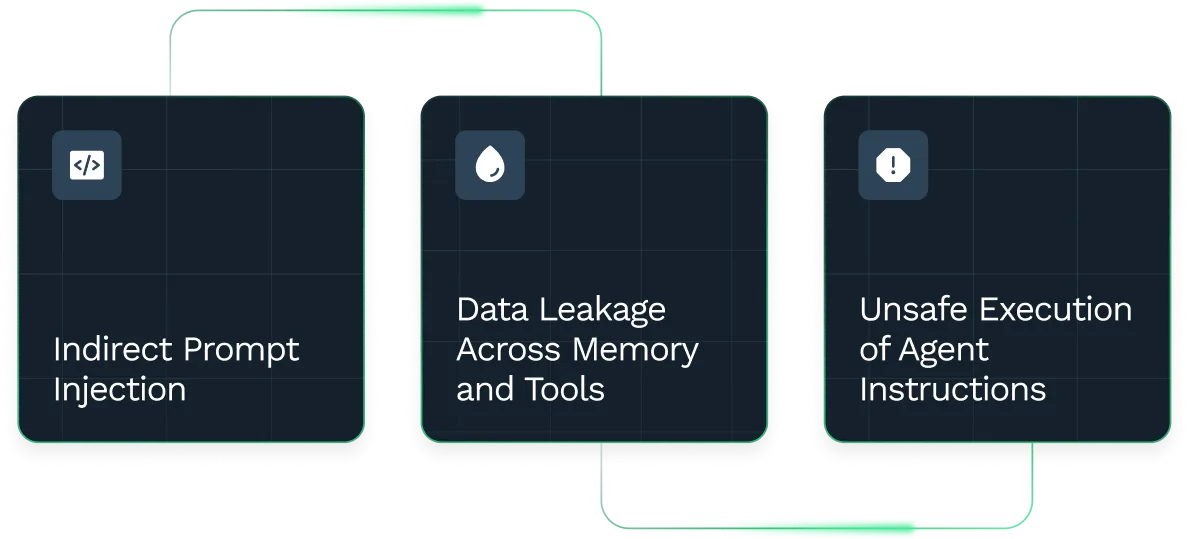
Agent workflows can be compromised invisibly
Indirect prompt injection can originate from untrusted inputs, external data, or retrieved context. These hidden injections corrupt memory, override system instructions, and lead agents to make harmful decisions.
Unknown agent capabilities can introduce security risk
Without visibility into the skills available to coding agents, security teams may not understand what actions agents can perform or whether those capabilities are appropriate for their environment.
How HiddenLayer protects agentic systems in real time
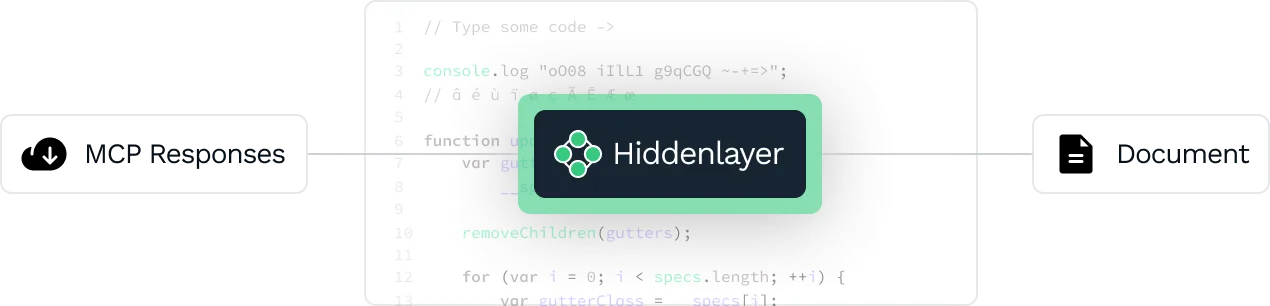
Indirect Prompt Injection Detection
Identify and block prompt injection hidden inside data, documents, MCP responses, or retrieved context before it impacts agent execution.

Memory and Context Safety
Detect unsafe memory recall, cross agent contamination, and exposed sensitive data before it becomes an instruction.

Tool Use and Action Inspection
Monitor agent actions and enforce runtime policy across APIs, MCP tools, code execution, communication tools, and filesystem operations.

MCP and Agentic Framework Traffic Inspection
Gain runtime visibility into agent behavior, reconstruct execution across sessions, and investigate activity across tools and workflows using LiteLLM proxy interception, SDK instrumentation, and gateway inspection.
Greater visibility and control across agentic AI
Understand agent behavior and available capabilities, reduce exposure to risky actions, and apply appropriate security controls.

Stop hidden prompt injections
Block indirect or covert injections originating from untrusted data.

Prevent unsafe autonomous actions
Ensure tool use, API calls, and multi step plans stay within approved guardrails.

Protect sensitive data
Detect and restrict leakage or memory corruption across agent workflows.

Gain visibility into agent behavior
Provide runtime visibility into complex multi-step agent workflows and reconstruct agent activity across tools and systems.
Secure emerging agent ecosystems
Support for leading frameworks including OpenAI, AWS Bedrock, and MCP based systems.

Understand and govern agent skills
Identify skills available to supported coding agents, evaluate their risks, and allow or deny usage based on organizational requirements.
Learn from the Industry’s AI Security Experts
Research, guidance, and frameworks from the team shaping AI security standards.


Ready to secure agent behavior and capabilities?
Gain visibility into agent activity, assess the risks of available coding-agent skills, and enforce controls to reduce unsafe behavior.